Key Points
- Transport for London said about 265,000 Oyster photocard customers may have had account details accessed.
- The incident was detected on 16 November 2026 after customers received unexpected account-registration emails.
- Potentially exposed information includes names, contact details, dates of birth and security questions and answers.
- TfL said passwords, bank and payment card details, journey information, and children’s names and dates of birth on Zip Oyster accounts were not compromised.
- The photocard website was taken offline, while customers can continue travelling and top up at station ticket machines.
- TfL notified the Information Commissioner’s Office and continues its investigation.
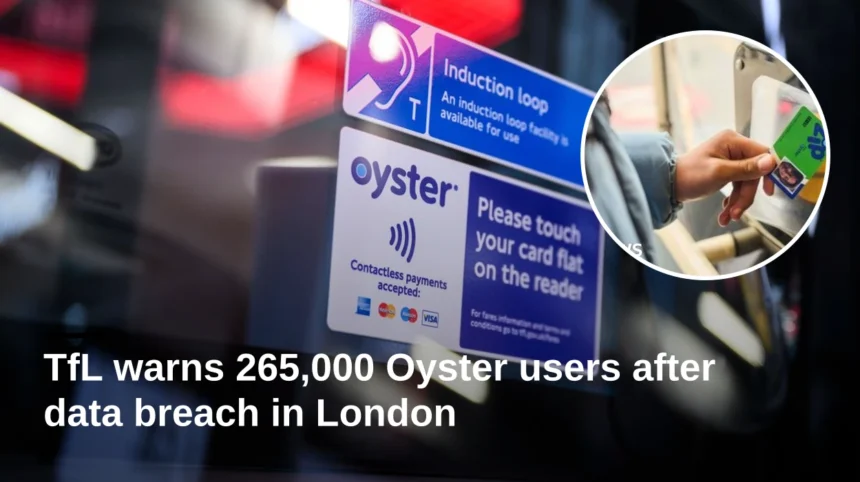
Hackney (East London Times) November 19, 2026 – Transport for London said around 265,000 Oyster photocard customers may have had personal account details compromised after suspicious activity was identified on its photocard website. TfL detected the incident on November 16, when customers received emails asking them to create accounts they already held. The authority removed the website while investigating and said the incident had been contained. TfL has contacted affected customers and notified the Information Commissioner’s Office.
What happened to the Oyster photocard website?
As reported by the BBC, Transport for London said suspicious activity enabled unauthorised access to personal information held in customer web accounts. The BBC reported that potentially affected information included names, email and home addresses, phone numbers, dates of birth, and security questions and answers.
The Independent reported that customers received unexpected emails prompting them to register for accounts despite already having photocard accounts. TfL said it acted by taking the photocard system offline to limit further access.
Shashi Verma, Transport for London’s Director of Technology Strategy and Revenue, said the authority became aware of the issue on November 16 and apologised to affected customers. TfL said its current assessment found no compromise of passwords, bank or payment card details, customer journey information, or the names and dates of birth of children with Zip Oyster cards.
Which Oyster customers may be affected?
Transport for London said potentially affected accounts include Zip Oyster cards for children aged five to 10, 11 to 15 and 16-plus; 18-plus Student Oyster cards; 18 to 25 Care Leaver Oyster photocards; 60-plus London Oyster photocards; Apprentice Oyster photocards; and Veterans’ Oyster photocards.
The BBC and Independent reported that the website remained offline, preventing customers from applying for or renewing photocards online while the investigation continued. TfL said affected customers had been contacted directly.
Can customers still travel and top up their cards?
Customers can continue using their Oyster photocards for travel, according to TfL. They can also top up their cards at ticket machines in London Underground and National Rail stations, although online photocard account access remains unavailable until the affected services are restored.
Customers who need to renew a photocard or query journey history can contact TfL Customer Services. TfL said it was working to restore the website as quickly as possible.
What is the background to the TfL data incident?
The incident followed emails that appeared inconsistent with customers’ existing Oyster photocard accounts. TfL identified the suspicious activity on November 16 and removed the photocard system while it assessed the extent of the unauthorised access.
Media reports said the potentially exposed data relates to web accounts rather than payment information or travel records. TfL said its early assessment excluded passwords, bank and payment card details, journey information, and children’s names and dates of birth on Zip Oyster accounts.
The authority said the speed of its response reduced the number of customers who may have been affected. TfL has notified the Information Commissioner’s Office and is continuing its investigation.
How could the incident affect Oyster photocard users?
Customers whose names, addresses, contact details, dates of birth or security answers may have been accessed could face an increased risk of targeted phishing or impersonation attempts. Families using Zip Oyster cards may be particularly alert to messages that appear to concern children’s travel accounts, although TfL said children’s names and dates of birth were not compromised.
Users should treat unexpected TfL messages cautiously, avoid entering information through unsolicited links, and use official TfL customer-service channels for account or travel queries. The immediate travel impact is limited because physical photocards remain usable and station ticket machines can be used for top-ups, but online applications, renewals and account management remain disrupted.